Get Certified with SCS: SOC 2 in Canada – Compliance and Audit Guide
Contact SCS: https://scscertification.com/contactus.php
Canadian businesses working with enterprise customers, cloud platforms and international technology partners may be asked to demonstrate how they protect customer information. For software companies, managed IT providers and businesses processing sensitive data, a SOC 2 report can help answer those questions by providing independent information about controls within a defined scope.
SOC 2 is especially relevant when customers want evidence of security practices, access management, incident response, system availability and other controls related to the services they use.
However, preparing for SOC 2 involves more than writing security policies. An organisation needs to understand its system boundaries, determine which Trust Services Criteria apply, establish appropriate controls and maintain evidence that reflects how those controls operate.
This guide explains SOC 2 for Canadian businesses, including Canadian privacy considerations, customer expectations, report types, readiness planning, cost factors and the relationship between SOC 2 and ISO 27001.
What Is SOC 2 in Canada?
SOC 2 is an examination and reporting framework developed by the American Institute of Certified Public Accountants (AICPA). It is used to examine controls at service organisations against applicable Trust Services Criteria.
These criteria address security and, where relevant to the engagement, availability, processing integrity, confidentiality and privacy.
For a Canadian organisation, a SOC 2 report can provide customers with structured information about the controls used to protect systems and deliver services. The report describes the defined system and the results of an independent examination within the agreed scope.
SOC 2 is not a Canadian government certification, and it is not a universal legal requirement for businesses operating in Canada. Nevertheless, a customer, procurement team or commercial contract may require a SOC 2 report before a supplier is approved.
Important terminology: SOC 2 is not an ISO-style certification scheme. The formal outcome is an attestation report issued by an appropriately qualified independent CPA firm. Businesses should distinguish readiness or consulting support from the independent examination itself.
Why Canadian Companies Consider SOC 2
The reasons for pursuing SOC 2 vary by organisation. Some businesses are responding to a specific customer request, while others want a more structured way to demonstrate how they manage security risks.
Enterprise customer requirements
Large customers often review a supplier's security arrangements before sharing confidential information or granting access to business systems.
A Canadian software company, for example, may be asked to explain how it restricts employee access to customer data, approves software changes, investigates incidents and monitors its production environment. A relevant SOC 2 report can help answer these questions within its stated scope.
The report does not automatically satisfy every customer's requirements. Buyers may also consider its age, report type, covered services, exceptions and other assurance documents.
International business opportunities
Canadian technology companies may serve customers in the United States and other markets where SOC 2 reports are commonly used during supplier assessments.
Having an appropriate report may help a business respond to due diligence requests and demonstrate that relevant controls have been independently examined. It does not guarantee that a customer will approve the supplier or award a contract.
More consistent internal controls
Preparing for SOC 2 can expose weaknesses in everyday processes. Access may not be reviewed regularly, changes may lack documented approvals, or vendor assessments may be inconsistent.
A readiness project gives the organisation an opportunity to assign responsibilities, establish repeatable procedures and retain evidence as work takes place.
The goal should be a control environment that can be maintained after the examination, rather than a collection of documents prepared only for review.
Canadian Privacy Laws and SOC 2
Canadian organisations need to understand the difference between a SOC 2 report and compliance with applicable privacy legislation.
SOC 2 examines controls against relevant criteria and within a defined scope. Privacy laws establish legal obligations that depend on the organisation's activities, location, sector and handling of personal information.
A SOC 2 report does not automatically establish compliance with every Canadian privacy requirement.
PIPEDA
The Personal Information Protection and Electronic Documents Act (PIPEDA) applies to certain private-sector organisations and commercial activities involving personal information. Its application depends on the circumstances, including the type of activity and relevant provincial legislation.
Organisations subject to PIPEDA need to understand their responsibilities for protecting personal information and managing applicable privacy obligations.
A SOC 2 examination may cover related security or privacy controls where relevant, but it does not replace a legal assessment of PIPEDA requirements.
Provincial privacy requirements
Depending on their activities, businesses may also need to consider provincial privacy legislation.
Examples include:
-
Alberta's Personal Information Protection Act (PIPA).
-
British Columbia's Personal Information Protection Act (PIPA).
-
Quebec's private-sector privacy legislation, including amendments commonly associated with Law 25.
The applicable requirements depend on the organisation's operations and the information it processes. Businesses should confirm their obligations with a qualified privacy or legal professional.
Financial services and other regulated sectors
Some organisations have additional obligations arising from their sector or regulatory status.
For example, federally regulated financial institutions should consider applicable Office of the Superintendent of Financial Institutions (OSFI) guidance, including Guideline B-13 on technology and cyber risk management.
A SOC 2 report may contribute to a wider assurance programme, but it should not be treated as a substitute for regulatory compliance.
Which Canadian Businesses May Need SOC 2?
SOC 2 is most relevant to service organisations whose customers need assurance about how their systems, services or information are managed.
SaaS and software companies
SaaS providers may store customer records, operate business applications and manage user accounts. Their customers may want assurance over access controls, software changes, incident response and monitoring.
The examination scope should identify the services and systems that customers need covered.
Cloud and managed IT service providers
Cloud providers and managed service providers may operate infrastructure, administer customer environments or hold privileged access to important systems.
Relevant controls may include identity management, security monitoring, vulnerability management, backup arrangements, incident handling and oversight of third-party services.
The report should make clear which services and dependencies are included.
Fintech businesses
Financial technology companies may process transactions, integrate with financial platforms or handle sensitive customer information. Enterprise customers may request independent assurance of relevant controls before approving a relationship.
SOC 2 may form part of the business's assurance programme alongside applicable contractual, privacy and sector-specific requirements.
Healthcare technology providers
Healthcare software and data-processing businesses may handle personal or sensitive information. Their customers may ask for evidence of access restrictions, information protection, incident handling and relevant privacy practices.
A SOC 2 report does not automatically establish compliance with every healthcare privacy requirement. Organisations should assess the applicable legal and contractual obligations separately.
Cybersecurity and data-processing businesses
Cybersecurity providers, data processors and technology consultancies may use SOC 2 reports to demonstrate that their own operations have been independently examined.
The report's value depends on whether the services and controls covered are relevant to the customer's actual concerns.
SOC 2 Type I and Type II: Choosing the Right Report
SOC 2 engagements generally result in either a Type I or Type II report.
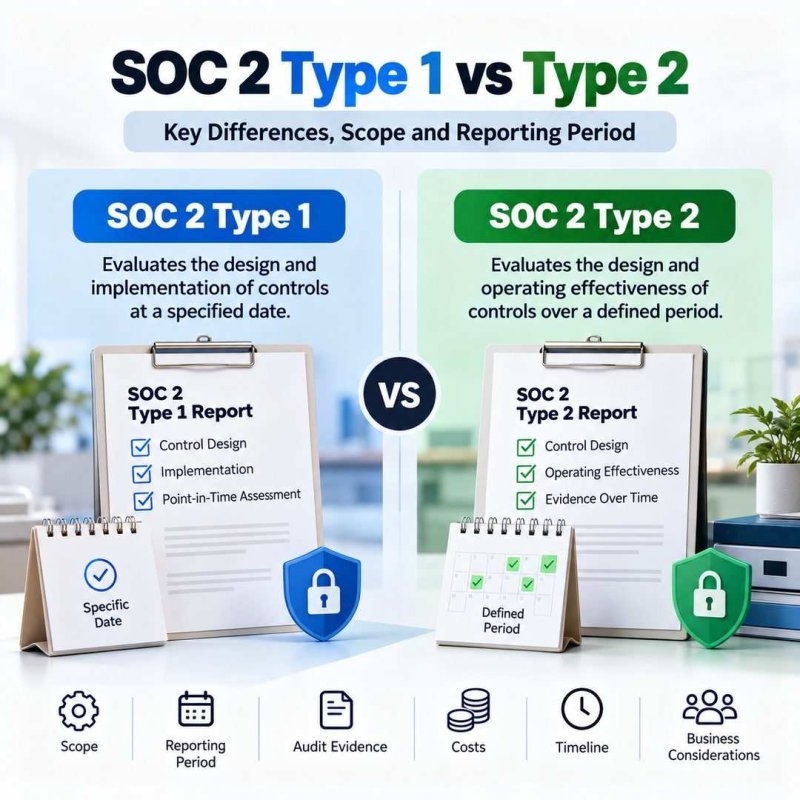
A Type I report addresses the design of controls and whether they are suitably implemented as of a specified date.
A Type II report addresses control design and examines operating effectiveness over a defined period.
The right option depends on customer expectations, the organisation's readiness and the purpose of the examination.
Before committing to an engagement, confirm whether the customer requires Type I or Type II, which services need to be covered, which criteria are relevant and how recent the report must be.
For a detailed comparison, see SCS's existing article:
SOC 2 Type I vs. Type II: Differences, Scope and Reporting Period
https://www.scscertification.com/blog/soc-2-type-1-vs-type-2-differences-scope-and-reporting-period/
This Canada guide focuses on Canadian business considerations rather than duplicating the full technical comparison.
Understanding the SOC 2 Trust Services Criteria
SOC 2 uses five Trust Services Criteria categories. Security is the common foundation; the other categories are included when relevant to the service commitments and examination scope.
Security
Security addresses protection against unauthorised access and other actions that could compromise systems or information.
Controls may include access restrictions, multifactor authentication, security monitoring, vulnerability management, incident response and controlled system changes.
Availability
Availability concerns whether systems are available for operation and use as committed or agreed.
Relevant controls may include capacity monitoring, backup arrangements, recovery planning and testing of restoration procedures.
Processing Integrity
Processing integrity relates to whether system processing is complete, valid, accurate, timely and authorised in accordance with relevant commitments and requirements.
This category may matter to businesses processing transactions, calculations, reports or other important data.
Confidentiality
Confidentiality concerns information designated as confidential under applicable commitments or agreements.
Controls may address access restrictions, secure information transfers, storage protections and appropriate handling throughout the information lifecycle.
Privacy
Privacy addresses the collection, use, retention, disclosure and disposal of personal information in accordance with applicable commitments and criteria.
Including Privacy in a SOC 2 examination does not, by itself, establish compliance with all Canadian privacy legislation.
Key Controls to Review Before a SOC 2 Examination
The exact controls depend on the organisation's services, risks, systems and selected criteria. However, several areas commonly deserve attention during readiness planning.
Identity and access management: Establish how access is approved, restricted, reviewed and removed when it is no longer required.
Risk assessment: Identify risks affecting the services in scope and document how the organisation addresses them.
Change management: Define how changes are requested, reviewed, approved, tested and deployed.
Incident response: Establish how incidents are identified, escalated, investigated, recorded and resolved.
Vendor management: Assess relevant third parties and determine how risks associated with outsourced services are managed.
Backup and recovery: Define responsibilities, retention arrangements and recovery procedures. Test recovery where appropriate and retain evidence.
Employee lifecycle: Address onboarding, role changes, access removal and relevant security training.
Security monitoring: Establish suitable monitoring and vulnerability management practices based on the systems and risks involved.
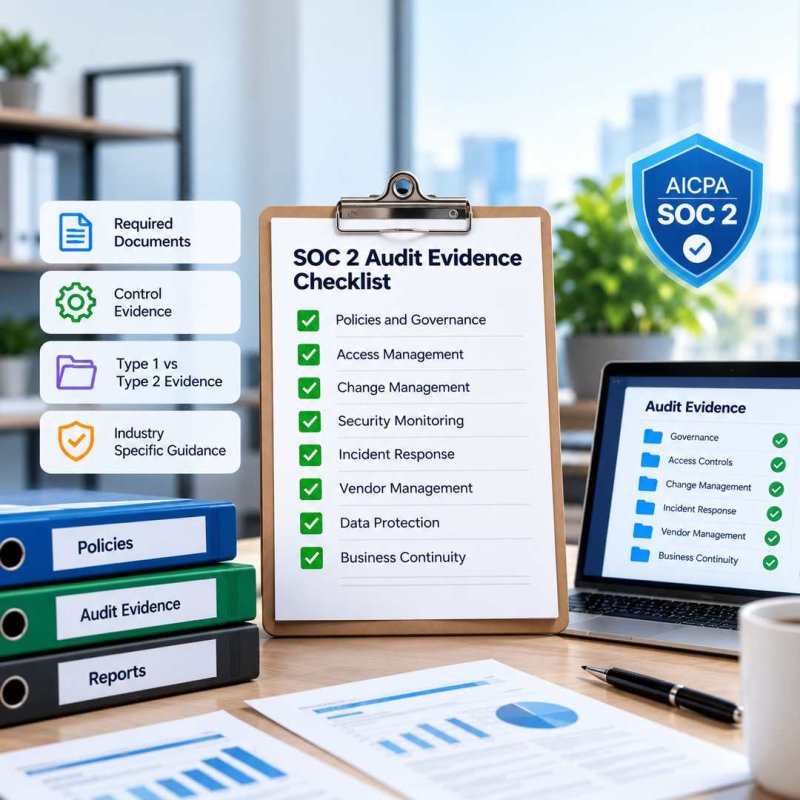
Policies and evidence: Maintain appropriate documentation and retain records demonstrating how controls operate.
A written policy alone does not necessarily demonstrate that a control is operating effectively. Depending on the control, useful evidence may include system records, access reviews, tickets, approvals, incident logs and test results.
For a practical documentation resource, see SCS's existing SOC 2 Audit Evidence Checklist: Documents, Controls and Requirements:
That article should remain the primary supporting resource for detailed evidence preparation.
How to Prepare for SOC 2 in Canada
A structured readiness process helps an organisation identify gaps and organise its work before the independent examination begins.
Step 1: Define the system scope
Identify the services, systems, teams, locations and information that need to be covered.
For example, a Canadian SaaS company may need to determine whether its scope includes the production platform, customer support processes, hosting arrangements and relevant internal systems.
The scope should reflect the services customers expect to see covered.
Step 2: Confirm customer requirements
Review contracts, security questionnaires and procurement requirements.
Confirm the requested report type, relevant criteria, covered services, expected reporting period and any additional assurance requirements.
This step can prevent an organisation from preparing for a report that does not meet its customers' needs.
Step 3: Review existing controls
Examine current security policies, access permissions, incident management, change management, vendor oversight and monitoring arrangements.
Record gaps, assign responsibilities and prioritise remediation according to risk and customer commitments.
Step 4: Implement improvements
Address the identified gaps and make sure that the revised controls are part of everyday operations.
Employees should understand their responsibilities, and control owners should know what evidence they need to retain.
Step 5: Organise evidence
Create a practical method for collecting and reviewing evidence.
Depending on the scope, this may include access approvals, access reviews, change tickets, security monitoring records, incident logs, vendor assessments, training records and backup test results.
Evidence should be traceable, relevant to the control and consistent with the activity it is intended to demonstrate.
Step 6: Consider readiness support
An organisation may use internal resources or engage an adviser to review its readiness, documentation and control gaps.
Readiness support should be distinguished from the independent examination. Confirm the provider's role, qualifications, deliverables and any independence requirements before proceeding.
Step 7: Engage the independent CPA firm
Discuss the intended scope, report type, criteria, evidence requirements and expected timeline with an appropriately qualified independent CPA firm.
The firm determines the examination procedures and issues its report in accordance with applicable professional requirements.
Step 8: Maintain controls after the report
SOC 2 should not be treated as a one-time documentation exercise. Organisations need to maintain relevant controls, retain evidence, monitor changes and address weaknesses as they arise.
The work required after the examination depends on the organisation's operating environment, customer commitments and future reporting plans.
SOC 2 vs. ISO 27001 in Canada
SOC 2 and ISO 27001 both relate to information security, but they have different purposes and outcomes.
ISO/IEC 27001 specifies requirements for an Information Security Management System (ISMS). An organisation can pursue certification through an appropriate certification body.
SOC 2 is an attestation examination based on applicable Trust Services Criteria. The formal outcome is a report issued by an appropriately qualified independent CPA firm.
| Comparison | SOC 2 | ISO 27001 |
|---|---|---|
| Main purpose | Examine controls against applicable Trust Services Criteria | Establish and maintain an information security management system |
| Formal outcome | SOC 2 report | ISO 27001 certificate following a successful certification audit |
| Scope | Defined services, systems and relevant controls | Defined ISMS scope and applicable requirements |
| Common customer interest | Assurance about service-organisation controls | Assurance about a structured information-security management system |
| Legal compliance | Does not replace applicable legal obligations | Does not replace applicable legal obligations |
Some organisations pursue both because customers have different assurance preferences. Others begin with the framework most closely aligned with their business objectives.
For more information about ISO 27001 in Canada, see SCS's existing guide:
ISO 27001 Certification in Canada – Complete ISO 27000 Series Guide
https://www.scscertification.com/blog/iso-27001-certification-in-canada-complete-iso-27000-series-guide/
The ISO 27001 article should remain focused on ISO certification, while this article targets SOC 2 and Canadian customer assurance requirements.
How Much Does SOC 2 Cost in Canada?
There is no single SOC 2 price that applies to every Canadian organisation. The total cost depends on the scope, complexity, report type and preparation required.
Factors that may affect cost include:
-
The number and complexity of systems and services in scope.
-
Whether a Type I or Type II report is required.
-
The relevant Trust Services Criteria.
-
The maturity of existing controls.
-
The availability and quality of evidence.
-
The use of third-party hosting and service providers.
-
The extent of readiness assistance required.
-
The scope and duration of the independent examination.
An organisation with established controls and well-maintained records may require less remediation than one building formal processes for the first time.
When comparing proposals, ask for a clear breakdown of readiness services, examination fees, report scope, expected timelines and any additional costs. Confirm which services are included and which party will perform the independent examination.
A quoted starting price should not be treated as a complete project cost until the scope and deliverables are clear.
Is SOC 2 Mandatory in Canada?
SOC 2 is not a universal legal requirement for every Canadian business.
However, a customer, procurement team or contract may require a SOC 2 report as a condition of doing business. Its practical importance therefore depends on the organisation's industry, target customers and services.
Applicable privacy laws and sector-specific requirements remain separate considerations. An organisation may need to meet those obligations whether or not it has a SOC 2 report.
Before deciding whether to pursue SOC 2, review customer contracts, procurement requirements, regulatory obligations and business objectives. Seek qualified legal advice when interpreting specific legal requirements.
Discuss Your SOC 2 Requirements with SCS
If your organisation operates in Canada and needs to understand its SOC 2 readiness requirements, begin by clarifying the services to be covered, customer expectations and the type of report required.
SCS can discuss your stated requirements and help you identify which support options may be appropriate. Confirm the exact scope of services available, the qualifications of relevant providers and the arrangements for independent examination before proceeding.
Contact SCS: https://scscertification.com/contactus.php
Important Note
This article provides general information and is not legal, regulatory or professional accounting advice. SOC 2 does not replace applicable Canadian privacy laws, regulatory requirements or contractual obligations. The scope and outcome of an examination depend on the organisation's circumstances and the independent CPA firm's work. Confirm the services offered by SCS before making a purchasing decision.
Contact SCS: https://scscertification.com/contactus.php
Need ISO Certification for Your Business?
Speak with our certification specialists to understand certification requirements, audit process, implementation timelines and accredited certification services.
Frequently Asked Questions
Contact SCS: https://scscertification.com/contactus.php