Reviewing a SOC 2 Report — Scope, Opinion, Exceptions and Customer Responsibilities
A supplier sends a SOC 2 report during procurement. Its cover looks relevant, but the service named in the system description differs from the product being purchased. Before accepting the report, the buyer needs to understand what assurance it actually provides.
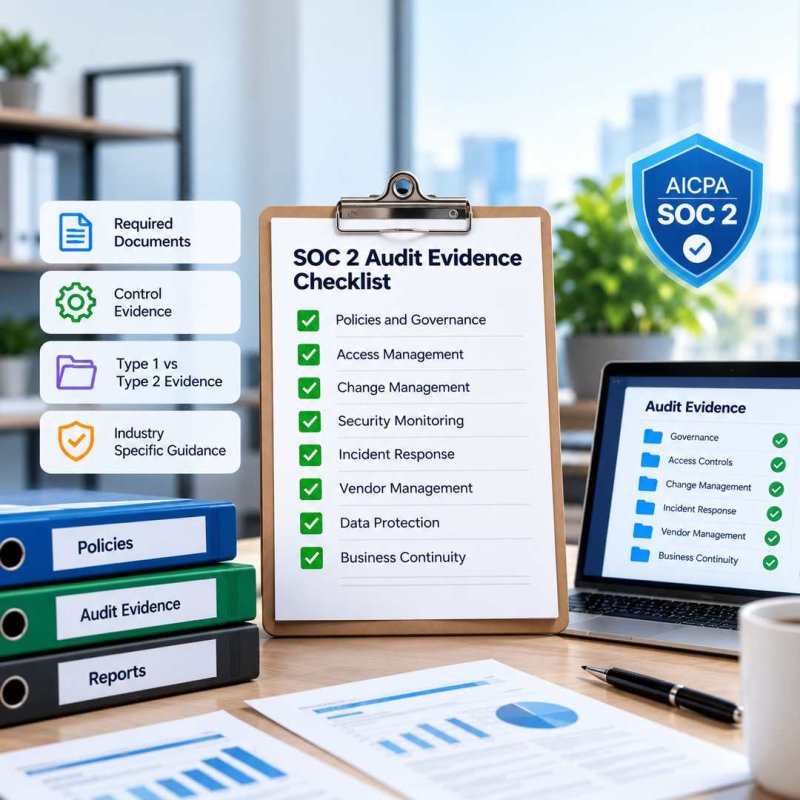
A useful SOC 2 report review connects the purchased service, reporting coverage, practitioner opinion and responsibilities that remain with the customer. It supports a documented acceptance decision rather than a tick beside “SOC 2 received.”
The AICPA illustrative report resource identifies major reporting components, including management's assertion, the system description, the service auditor's report and Type 2 control tests and results. Follow the actual report and its restrictions when reviewing it.
Confirm relevance before interpreting individual findings
Identify the legal entity, described service, report type and covered date or period. Compare them with the proposed purchase and the customer's assurance requirement. A shared group name or logo does not establish that the report concerns the relevant product.
Check whether important locations, outsourced activities or components are addressed within the reporting arrangement. Record differences and questions for the supplier rather than assuming favourable coverage from the cover page.
Use the established Type 1 versus Type 2 guide if report-type terminology needs clarification. The task here is deciding how a received report relates to a particular purchase.
Use a review record with a clear decision owner
|
Review area |
Information to retain |
Buyer question |
|
Identity and service |
Report entity, product and system description |
Is this the supplier service being purchased? |
|
Time coverage |
Type, relevant dates and known changes |
Does the information meet the actual requirement? |
|
Scope |
Categories, important boundaries and dependencies |
Which concerns remain outside the report? |
|
Results |
Opinion, relevant exceptions and accompanying information |
What requires further evaluation or follow-up? |
|
Responsibilities |
Complementary controls and relevant user duties |
Can the customer perform what is expected of it? |
|
Acceptance |
Reviewer, decision, conditions and follow-up |
Who owns the remaining risk or unanswered questions? |
This is an illustrative buyer worksheet. It does not replace professional interpretation of a report or require acceptance of any particular opinion.
Read the opinion and exceptions in context
Read the practitioner's report rather than relying on a supplier's marketing summary. Identify the conclusion and any matters relevant to its interpretation. Then consider control-test results and exceptions in relation to the described system and the buyer's use.
An exception requires context: what activity and population were involved, when it occurred and what the report actually says. A management response is useful information, but its status and relationship to the practitioner's work need to remain clear.
Avoid treating all exceptions as either automatic rejection or insignificant administration. The buyer's authorised risk or procurement process should determine the appropriate response using the relevant facts and advice.
Review provider dependencies and customer controls
Where a subservice organisation is relevant, understand how the report addresses it. Identify important complementary controls or assumptions affecting the service and whether further information is needed.
Allocate relevant customer responsibilities internally. If the report assumes user access administration or a particular customer configuration, determine who in the buying organisation can confirm the applicable arrangements. Receiving the supplier's report does not implement those activities for the customer.
AICPA's Description Criteria resource provides authoritative context for the system description. Use it as a reference rather than rewriting the supplier's scope during a buyer review.
Distinguish report coverage from later information
The covered period, report issue date and buyer review date are different. Ask about significant changes relevant to the purchase where the report alone does not answer the current question.
A management bridge letter can provide information about a subsequent gap. It should be identified as management information rather than treated as an extension of the independent examination. KPMG's control-reporting handbook discusses bridge letters as unaudited information about changes during such a gap. That reference is contextual guidance, not a universal acceptance period for SOC 2 buyers.
Do not apply an invented expiry date or standard bridge-letter duration to every report. Evaluate the actual buyer requirement and seek appropriate clarification about recency and change.
Share and retain the report appropriately
Follow restrictions on use and distribution, relevant confidentiality arrangements and the organisation's access process. Agree who may review the report and whether any proposed extracts or redacted version are appropriate.
Keep the acceptance record and follow-up separate from public sales material. Avoid publishing detailed report contents or implying that a report provides unrestricted public assurance. The AICPA SOC resources explain the broader professional reporting context.
An illustrative product mismatch
A fictional Canadian buyer purchases a new analytics service from an Indian supplier. The supplied report describes another platform. Some infrastructure is shared, but the buyer cannot determine whether its intended service is within the report.
The reviewer records the mismatch, asks the supplier for clarification and refers the unresolved matter to the buyer's authorised decision-maker. It does not convert shared infrastructure into assumed service coverage.
The Canada and India SOC 2 guides provide country enquiry context. This fictional example does not establish report acceptance or a practitioner conclusion.
Discuss the actual report question with SCS
Explain whether the enquiry concerns a supplier report, a customer acceptance question or preparation for your own engagement. Identify the service and the issue without attaching unrestricted confidential material to a general form.
For separate provider-selection questions, refer to the existing UAE SOC 2 provider guide. Contact SCS to clarify the support being requested and any independent professional interpretation needed.
Need ISO Certification for Your Business?
Speak with our certification specialists to understand certification requirements, audit process, implementation timelines and accredited certification services.